Major Cyberattack
Ransom Demand Following Brenner Tunnel Cyberattack
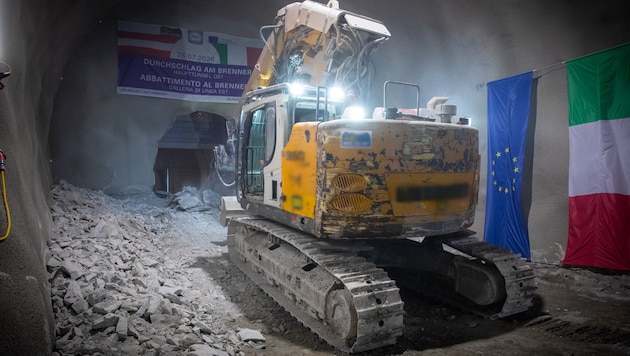
New details were released on Monday following the cyberattack on BBT SE, the operating company of the Brenner Base Tunnel. According to the report, unauthorized access was gained to a data exchange server. Internal IT systems and construction operations were not affected, based on current information, the company said. A ransom demand has also already been received. Investigations are ongoing.
 Kronen Zeitung als bevorzugte Google-Quelle hinzufügen
The cyberattack took place on October 17. As the company itself officially announced on Monday, unknown individuals gained unauthorized access to a server used for data exchange between BBT SE and Italian contractors.
Affected data source isolated
“The volume of data stored on the server amounts to 812 gigabytes,” the statement said. Immediately after the incident came to light, BBT SE “initiated the necessary security measures. The affected data source was disconnected from the network and isolated, IT security protocols were activated, and external cybersecurity experts were commissioned to conduct a forensic analysis,” the company said.

BBT SE can confirm that a ransom demand was received in connection with the cyberattack.
Die BBT SE in einer Aussendung
Perpetrators Demand Ransom
Experts are also monitoring whether stolen data is being published online. To date, no such publications have been detected. “Any attempt by the hackers to contact BBT SE has been—and will continue to be—reported to the relevant investigative authorities,” the company emphasized in a press release.
The perpetrators have, in fact, already attempted to make contact: “BBT SE can confirm that a ransom demand has been received in connection with the cyberattack.” Since the investigation is ongoing, “no information can currently be provided regarding the content of the demand or further details,” the statement continued.

No Impact on Construction Operations
Based on current information, the incident is not expected to have any operational consequences for the major Brenner Base Tunnel project. According to BBT SE, the attack was limited to the external data exchange server. The company’s internal IT systems were not affected.
Construction work is also continuing without restrictions. The safety of ongoing construction operations was not compromised at any time. Likewise, there is no risk to future rail operations.
Technical Documents and Tender Data
The affected BBT SE data consists of technical and administrative documents, most of which were already publicly available, including, for example, tender documents and surveying data. The Italian contractors involved have been informed. Based on current information, Austrian contractors are not affected.
BBT SE is currently unable to provide further details regarding the scope and nature of the contractors’ data. This is the subject of the investigation.
BBT SE has informed the relevant Italian authorities and initiated the necessary legal steps.
This article has been automatically translated,
read the original article here.




Willkommen in unserer Community! Eingehende Beiträge werden geprüft und anschließend veröffentlicht. Bitte achten Sie auf Einhaltung unserer Netiquette und AGB. Für ausführliche Diskussionen steht Ihnen ebenso das krone.at-Forum zur Verfügung. Hier können Sie das Community-Team via unserer Melde- und Abhilfestelle kontaktieren.
Hinweis in eigener Sache: Das krone.at-Forum präsentiert sich ab sofort in neuem Design! Wir freuen uns über konstruktives Feedback. Damit die Diskussionen in den Kommentarbereichen beim jeweiligen Thema bleiben, können Sie uns Rückmeldungen hier hinterlassen.
User-Beiträge geben nicht notwendigerweise die Meinung des Betreibers/der Redaktion bzw. von Krone Multimedia (KMM) wieder. In diesem Sinne distanziert sich die Redaktion/der Betreiber von den Inhalten in diesem Diskussionsforum. KMM behält sich insbesondere vor, gegen geltendes Recht verstoßende, den guten Sitten oder der Netiquette widersprechende bzw. dem Ansehen von KMM zuwiderlaufende Beiträge zu löschen, diesbezüglichen Schadenersatz gegenüber dem betreffenden User geltend zu machen, die Nutzer-Daten zu Zwecken der Rechtsverfolgung zu verwenden und strafrechtlich relevante Beiträge zur Anzeige zu bringen (siehe auch AGB). Hier können Sie das Community-Team via unserer Melde- und Abhilfestelle kontaktieren.