Cyberattack
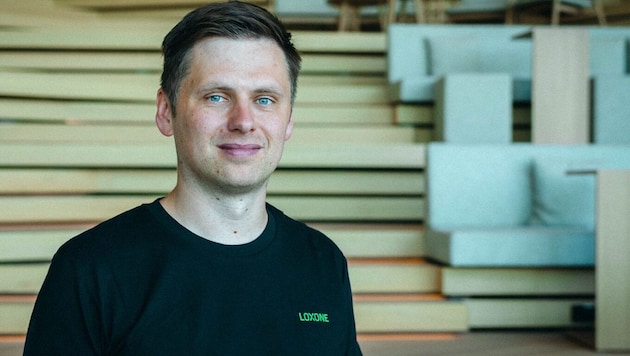

Following the cyberattack on Loxone, the globally active smart-home specialist based in the Mühlviertel region, the company is in a state of emergency. A crisis team is working around the clock to restore the systems. In an interview with the “Krone,” CEO Florian Wöss explains the current status of customer security and how the past few hours have been for him personally.
 Kronen Zeitung als bevorzugte Google-Quelle hinzufügen
The attack was apparently discovered in the early hours of Sunday morning: Instead of the usual website, visitors to loxone.com found a message from the alleged extortionists. It reads: “We have your data.”
As reported, a hacker group calling itself “Samurai” is believed to be behind the message. The alleged perpetrators claim to have copied and encrypted a total of 201.6 gigabytes of data from the company’s internal network. This is said to include customer data, support requests, personnel records, and information on more than 300,000 registered Miniservers.
Extortionists Threaten to Release Data
To emphasize their demands, the extortionists are threatening to publish the data once a deadline has passed. They are instructing Loxone to contact them via an encrypted messaging app to negotiate a ransom payment. Whether data on this scale was actually stolen has not yet been confirmed.
“Working in shifts to restore systems”
In an interview with the “Krone,” Florian Wöss, President of Loxone Electronics GmbH, now provides insight into the events of the past few hours. “As has been reported, we immediately deployed a team of 25 people internally yesterday,” says the CEO. The crisis team also includes the company’s owners and top management. Since then, work has been ongoing around the clock in shifts to restore the systems.
Wöss hasn’t gotten much sleep lately. When asked how long he slept from Sunday into Monday, he replies, “Two hours.” Numerous employees also worked through the night. Support is coming from external IT security experts who have been working with Loxone for years and regularly review the systems.
“We Know How the Attackers Got Into Our System”
And there’s been a first crucial breakthrough: “We know exactly how the attacker gained access to our system,” says Wöss. The attack vector has since been investigated and confirmed in collaboration with external IT forensic experts. For understandable reasons, the company CEO does not wish to reveal exactly how the hackers proceeded at this time.
The affected IT systems were initially isolated after the attack was discovered. They are now set to be gradually brought back online. Wöss expects normal operations to resume in the course of the week.
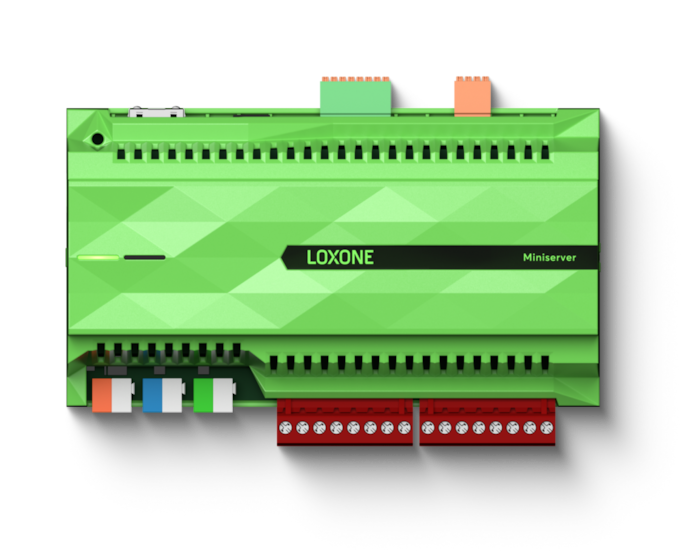
“The Loxone Miniserver does not require internet access”
It is particularly important to the company to reassure its customers. Loxone emphasizes that the smart home installations and the online services necessary for their operation were not affected by the cyberattack.
A key reason for this is the deliberately chosen architecture of Loxone’s technology. The Miniservers—the control centers of the smart homes—operate locally and independently of the company’s IT infrastructure. They require neither an internet connection nor access to Loxone’s servers to function.
An IT expert also confirmed to the “Krone” that owners of Loxone smart homes are now benefiting from a deliberate decision the company made in the past. This is because remote access to the Miniservers is provided via a proxy service.
Wöss also confirms that Loxone does not centrally store any login credentials for the Miniservers. These are stored exclusively on-site with the respective customer. Even if hackers were to obtain information such as the devices’ MAC addresses, they would not be able to access the systems with that information alone. “This is my home, my data,” says Wöss, explaining the company’s philosophy.
It remains unclear whether the attackers actually stole more than 200 gigabytes of data, as claimed. Loxone announced that it would directly notify individuals whose data has been verifiably compromised. The relevant authorities have also been notified.
1,300 employees at 48 locations worldwide
Loxone was founded in 2009 by Thomas Moser and Martin Öller in Kollerschlag (Rohrbach district) and is now one of the world’s leading providers of home and building automation. The company’s technology controls, among other things, lighting, heating, shading, and security systems in residential homes, hotels, and commercial buildings. The globally active corporate group now employs more than 1,300 employees at 48 locations. More than 80 percent of its business comes from exports.
This article has been automatically translated,
read the original article here.




Willkommen in unserer Community! Eingehende Beiträge werden geprüft und anschließend veröffentlicht. Bitte achten Sie auf Einhaltung unserer Netiquette und AGB. Für ausführliche Diskussionen steht Ihnen ebenso das krone.at-Forum zur Verfügung. Hier können Sie das Community-Team via unserer Melde- und Abhilfestelle kontaktieren.
Hinweis in eigener Sache: Das krone.at-Forum präsentiert sich ab sofort in neuem Design! Wir freuen uns über konstruktives Feedback. Damit die Diskussionen in den Kommentarbereichen beim jeweiligen Thema bleiben, können Sie uns Rückmeldungen hier hinterlassen.
User-Beiträge geben nicht notwendigerweise die Meinung des Betreibers/der Redaktion bzw. von Krone Multimedia (KMM) wieder. In diesem Sinne distanziert sich die Redaktion/der Betreiber von den Inhalten in diesem Diskussionsforum. KMM behält sich insbesondere vor, gegen geltendes Recht verstoßende, den guten Sitten oder der Netiquette widersprechende bzw. dem Ansehen von KMM zuwiderlaufende Beiträge zu löschen, diesbezüglichen Schadenersatz gegenüber dem betreffenden User geltend zu machen, die Nutzer-Daten zu Zwecken der Rechtsverfolgung zu verwenden und strafrechtlich relevante Beiträge zur Anzeige zu bringen (siehe auch AGB). Hier können Sie das Community-Team via unserer Melde- und Abhilfestelle kontaktieren.